Mastering DevSecOps Orchestrating Security and Compliance in CI/CD Pipelines
DevSecOps: Integrating Security into the Continuous Pipeline
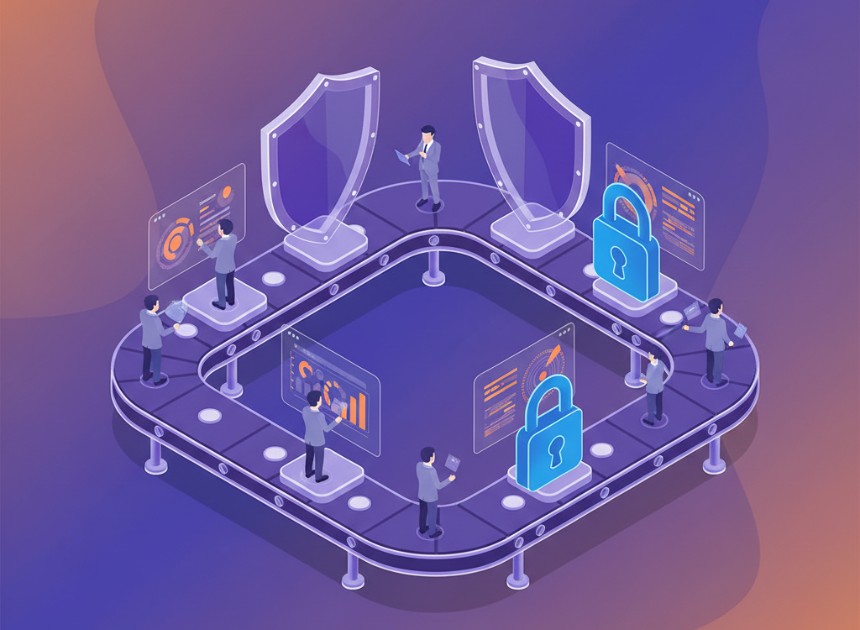
In the modern digital landscape, the pressure to deliver software at high velocity often creates a friction point between development teams and security departments. Traditional security models, which treat compliance as a final hurdle before release, are no longer viable. At iExperts, we advocate for the Shift Left philosophy, where security is not a gatekeeper but an integral part of the continuous pipeline. By automating compliance, organizations can maintain the rigorous standards required by NIST CSF 2.0 and ISO 27001:2022 without sacrificing a single day of development speed.
The iExperts Approach to Automated Governance
Our methodology focuses on transforming manual checklists into executable code. This evolution allows for real-time validation of security controls during the build and deploy phases. By leveraging automated tooling, iExperts ensures that every piece of code entering the production environment has already been vetted against global standards such as PCI DSS 4.0 and GDPR.
- Static Analysis (SAST): Identifying vulnerabilities within the source code before execution.
- Dynamic Analysis (DAST): Testing the application in its running state to find security flaws that SAST might miss.
- Infrastructure as Code (IaC) Scanning: Ensuring that the cloud environment is configured according to best practices and compliance frameworks.
Key Deliverables for a Secure Pipeline
When iExperts implements a DevSecOps strategy, we focus on tangible outcomes that empower both developers and risk managers. These deliverables ensure that security is measurable and transparent across the entire organization.
- Automated Vulnerability Reporting
- Compliance-as-Code Policy Engine
- Real-time GRC Dashboard Integration
- Secured Container Orchestration
"Security should be like brakes on a high-performance car; they are not there to slow you down, but to allow you to go faster with the confidence that you can stop when necessary."
Pro Tip
Always integrate Software Composition Analysis (SCA) into your early CI stages. This allows you to detect insecure third-party libraries and open-source dependencies before they are baked into your architecture, drastically reducing your attack surface and meeting ISO 42001 requirements for AI and software supply chain integrity.
The journey to a fully integrated DevSecOps model requires a cultural shift as much as a technical one. By partnering with iExperts, your organization can bridge the gap between agility and security, ensuring that every deployment is a secure deployment. We move beyond manual audits into a world of continuous assurance, where compliance is an automated byproduct of your development excellence.